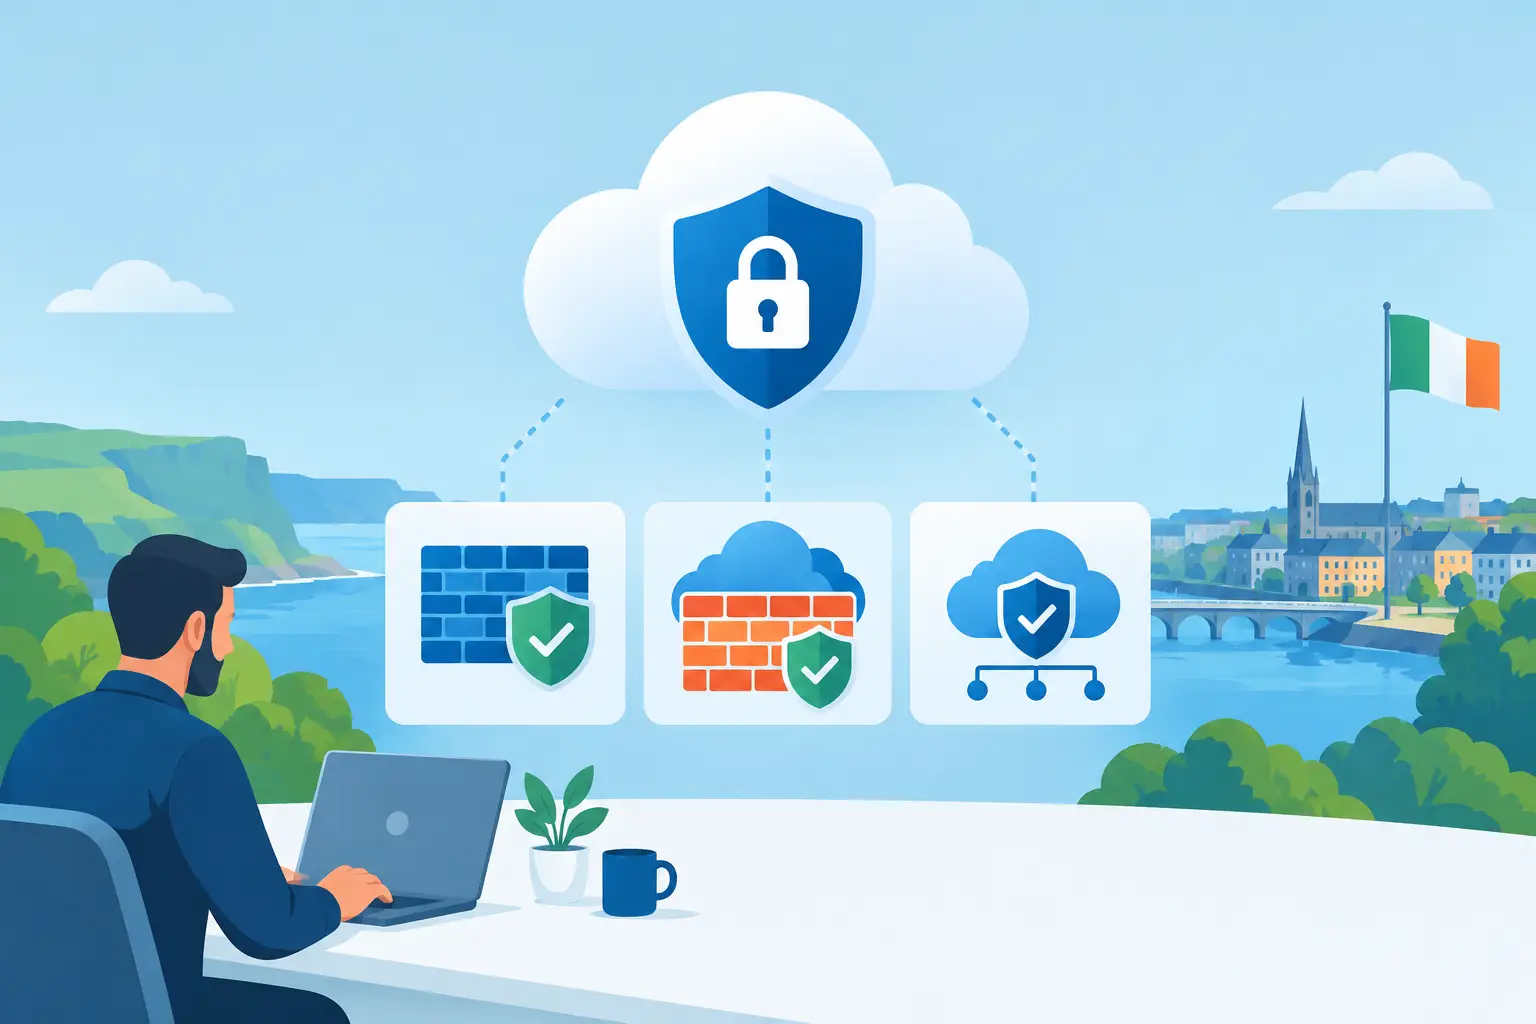

A cloud firewall comparison should start with the disruption you are trying to prevent, not a list of technical features. For most small and medium-sized businesses, the real question is whether staff can work safely from the office, home and customer sites without opening a path to ransomware, data loss or costly downtime.
Traditional firewalls were designed around a clear boundary: the office network. That boundary has changed. Microsoft 365, cloud applications, remote users, mobile devices and branch locations all create traffic that may never pass through a single office firewall. A cloud firewall can extend protection to those connections, but the right model depends on how your business operates and who will manage it.
What a cloud firewall actually does
A cloud firewall is a security service delivered from cloud infrastructure rather than solely from an appliance in your comms cabinet. It inspects and controls traffic according to security policies, helping to block malicious activity, restrict risky websites and applications, and protect access to business systems.
The term covers several approaches. Some providers offer a firewall hosted in the cloud to protect cloud servers and workloads. Others deliver secure web gateways and firewall-as-a-service for users accessing the internet and software-as-a-service platforms. There are also managed firewall services, where a specialist configures, monitors and maintains either cloud-based or on-site security.
This distinction matters. A product built to protect virtual servers in Azure or AWS is not automatically the best way to secure laptops used by a hybrid workforce. Equally, a cloud web security service will not replace the local network controls required for an office with servers, VoIP phones, printers and guest Wi-Fi.
Cloud firewall comparison: the models that matter
For an SME, comparing platforms by headline specifications alone can be misleading. Assess what is protected, where people work, how policies are managed and what happens when something goes wrong.
| Approach | Best suited to | Main advantage | Trade-off to consider | |—|—|—|—| | Cloud-native firewall | Businesses hosting servers or applications in public cloud platforms | Controls traffic between cloud workloads and the internet | Does not fully protect office networks or remote devices on its own | | Firewall-as-a-service | Hybrid teams using cloud applications from multiple locations | Consistent internet security wherever users connect | Relies on sound identity, device and internet connectivity management | | Next-generation firewall appliance with cloud management | Offices needing local network protection and visibility | Protects on-site devices, Wi-Fi, voice and local systems | Hardware still needs configuration, updates and replacement planning | | Managed firewall service | SMEs without dedicated security specialists | Ongoing monitoring, tuning and expert support | Service scope and response responsibilities must be clearly defined |
In practice, many businesses need a combination. An office may require a next-generation firewall at the network edge, while remote users need cloud-delivered protection when they are away from that network. Cloud servers need their own tightly controlled rules. Trying to force one tool to cover every scenario can leave gaps or create an unnecessarily complicated setup.
Protection quality is more than blocked ports
Basic firewall rules allow or deny traffic by address, port and protocol. That remains necessary, but modern threats often use legitimate web services, compromised user accounts and encrypted traffic. A meaningful comparison should therefore include intrusion prevention, web filtering, malware detection, DNS security, application control and encrypted traffic inspection where appropriate.
The word “appropriate” matters. Decrypting traffic can improve visibility, but it needs careful configuration to avoid privacy concerns, application failures and unnecessary performance impact. A security provider should help set sensible exclusions and policies rather than enable every feature without considering the business.
Email security, multi-factor authentication and endpoint protection also remain essential. A firewall reduces exposure, but it cannot prevent a user approving a fraudulent sign-in prompt or sending data to the wrong recipient. Security works best as a coordinated set of controls, not as a single purchase.
Management is often the deciding factor
Cloud-managed security can give businesses one place to view policies, alerts, users and sites. That is useful when an organisation has several offices, remote staff or no internal network engineer. Changes can be made centrally, and software updates are generally easier to coordinate.
However, a portal does not equal effective management. Someone still needs to decide which alerts are meaningful, review blocked activity, maintain access rules and respond to suspected incidents. Poorly maintained rules commonly become a risk over time, particularly where former staff, old suppliers or temporary remote access arrangements remain active.
When reviewing a managed option, ask who owns day-to-day policy changes and how quickly urgent requests are handled. Clarify whether the provider monitors alerts around the clock or only during business hours, what escalation looks like, and whether incident support is included. These details have a greater effect on resilience than a polished dashboard.
How to compare cost without missing the real expense
Cloud firewall pricing is often subscription-based. Costs may be calculated per user, per site, by bandwidth, by cloud workload or through a managed monthly service. That can be easier to budget for than buying an appliance outright, but it also means the comparison needs to cover the full operating cost over several years.
Check whether licences include advanced threat prevention, secure remote access, logging retention and technical support. Some lower entry prices cover basic filtering but charge extra for the capabilities that provide meaningful protection. Data processing and log storage can also affect cloud costs as traffic volumes grow.
An appliance-led solution has a different profile. There may be upfront hardware, installation and renewal costs, followed by subscriptions for security services and support. It can be an efficient choice for a stable office network, especially where local performance and direct control are priorities. Yet it should not be treated as a set-and-forget purchase. Hardware ages, subscriptions expire and cyber threats change.
The financial impact of downtime deserves equal attention. If a security incident stops staff accessing email, files, phones or customer systems, the cost reaches beyond the firewall invoice. Lost working hours, delayed customer service, recovery effort and reputational damage can quickly outweigh a sensible managed security investment.
Questions to ask before choosing
A useful comparison meeting should focus on your environment. Start with where your data sits, how staff access it and which systems cannot be unavailable. Then establish whether the proposed service protects office traffic, remote traffic, cloud workloads or all three.
Ask how the solution works with Microsoft 365, identity management, endpoint protection and backup. If a user device is compromised, can access be limited quickly? If an office connection fails, is there a secure failover option? If ransomware is suspected, who can help isolate systems and support recovery?
It is also worth asking for plain-language confirmation of responsibility. Your business remains responsible for access decisions and user behaviour, while a managed IT partner may operate the technical controls. The boundary should be documented, tested and understood before an incident, not during one.
Avoid buying for a threat you do not have
Larger platforms can offer impressive capabilities, but more features can mean more administration and more opportunities for configuration mistakes. A ten-person professional services firm has different requirements from a multi-site business with production systems, guest networks and regulated customer data.
That does not mean smaller businesses should accept weaker protection. It means security should be proportionate, properly configured and actively supported. The best choice is the one that protects the systems you rely on, fits the way your people work and can be maintained consistently.
Building protection around business continuity
A firewall should support continuity planning, not sit separately from it. Its policies need to reflect which services are critical, which staff require remote access and how your business will communicate if a primary connection or system is unavailable.
For Dublin SMEs with limited internal IT resources, a managed approach can reduce the burden of maintaining those controls while keeping an experienced team available when changes or incidents arise. Host-It can help businesses assess existing network security, cloud access and recovery arrangements as part of a practical, wider IT support plan.
Choose the firewall model that your team can operate confidently on an ordinary Tuesday and rely on during a difficult one. That is where security becomes a genuine safeguard for productivity, rather than another system waiting to be managed.